
Hardware wallet maker Keystone has confirmed a security breach that exposed customers’ names, home addresses and purchase details, raising concerns about phishing scams and physical threats against cryptocurrency holders.
Summary
- Keystone confirmed that attackers obtained customer shipping information following unauthorized website access.
- The exposed records included names, contact details, addresses, purchased products and prices.
- Keystone said recovery phrases, private keys, passwords and payment information were not compromised.
- The incident raises phishing and physical security concerns similar to those following Ledger’s 2020 breach.
- Keystone has blocked the unauthorized access and begun notifying affected customers.
According to Keystone’s October 24 disclosure, the company detected unauthorized access to its official website on October 20 and confirmed the theft three days later after reviewing application programming interface activity with Shopify, its e-commerce provider.
“We owe you an apology,” the company said, acknowledging that customers had trusted it to protect their personal information.
Meanwhile, the incident affected information collected during hardware wallet purchases, including contact details, shipping addresses, products ordered and their prices. Keystone said payment card information, bank details, recovery phrases, private keys and wallet passwords were not exposed.
Keystone confirms customer data theft through website breach
Keystone said it blocked the unauthorized access, corrected the vulnerability and opened an investigation after confirming that an outside party had obtained customer shipping information.
The company has begun emailing affected customers and promised a detailed report explaining the incident.
However, its initial statement did not identify the attackers, disclose the number of affected customers or specify when the unauthorized access first began.
The company has not explained whether the attacker exploited a stolen API credential, an application vulnerability or another weakness in its website infrastructure.
Keystone’s reference to Shopify API activity identifies information investigators examined when confirming the theft. It does not establish that Shopify’s underlying platform was compromised.
Shopify provides online store infrastructure and programming interfaces that allow merchants and authorized applications to manage customer information and orders.
Depending on the permissions granted, an application connected to a merchant’s store may access sensitive records. Keystone has not disclosed which credentials or permissions were involved in this incident.
Why leaked wallet addresses create physical security risks
Although Keystone said customers’ cryptocurrency credentials remained secure, its disclosure warned that attackers could misuse their personal details.
Names and home addresses can help criminals identify people who have purchased hardware wallets, while order information can make fraudulent messages appear more convincing.
Keystone specifically warned about scammers impersonating the company through email, telephone calls, text messages or physical mail.
Potential scams include fake refunds, replacement devices and requests to correct delivery information.
“NEVER share your recovery phrase or private keys,” the company warned, adding that customers should never enter recovery phrases into devices they did not order.
The company advised users to visit its website directly and contact official support when receiving suspicious communications.
Security developer Taylor Monahan, known online as Tay, warned that leaking hardware wallet buyers’ shipping information could expose customers to physical threats, including robbery and kidnapping.
Her comments highlighted concerns about so-called wrench attacks, in which criminals use threats or violence to force cryptocurrency holders to surrender access to their assets.
There is no confirmed evidence in Keystone’s disclosure that the stolen information has already resulted in physical attacks.
Ledger’s 2020 breach shows how stolen addresses can persist
Keystone’s incident recalls the customer information breach disclosed by rival hardware wallet maker Ledger in July 2020.
According to Ledger’s original investigation, an attacker accessed part of its e-commerce and marketing database through an API key.
Ledger initially identified approximately one million compromised email addresses and detailed personal information belonging to around 9,500 customers.
When the stolen database appeared publicly in December 2020, the company acknowledged a larger exposure involving roughly 272,000 records containing names, postal addresses and telephone numbers.
Ledger maintained that its hardware wallets and customers’ private keys had not been compromised.
The stolen information nevertheless became a concern because criminals could use identifying details to target buyers outside the company’s systems.
In April 2025, crypto.news reported on fraudulent letters sent to Ledger customers. The letters impersonated the manufacturer and instructed recipients to scan QR codes before entering their recovery phrases.
Investigators had not established whether every reported letter originated from the 2020 database.
More recently, an October 2026 security investigation examined potentially altered devices distributed through a third-party reseller, illustrating a separate risk involving physical wallet supply chains.
Keystone faces questions over breach scale and customer protection
Former Binance chief executive Changpeng Zhao reacted to Keystone’s announcement with a brief warning: “Stay SAFU!”
Blockchain commentator Chain INK circulated a list of reported hardware wallet security incidents during 2026, covering customer information leaks, phishing attempts, software flaws and suspected device tampering.
Those incidents involved different attack methods and should not be counted as equivalent breaches of hardware wallet encryption.
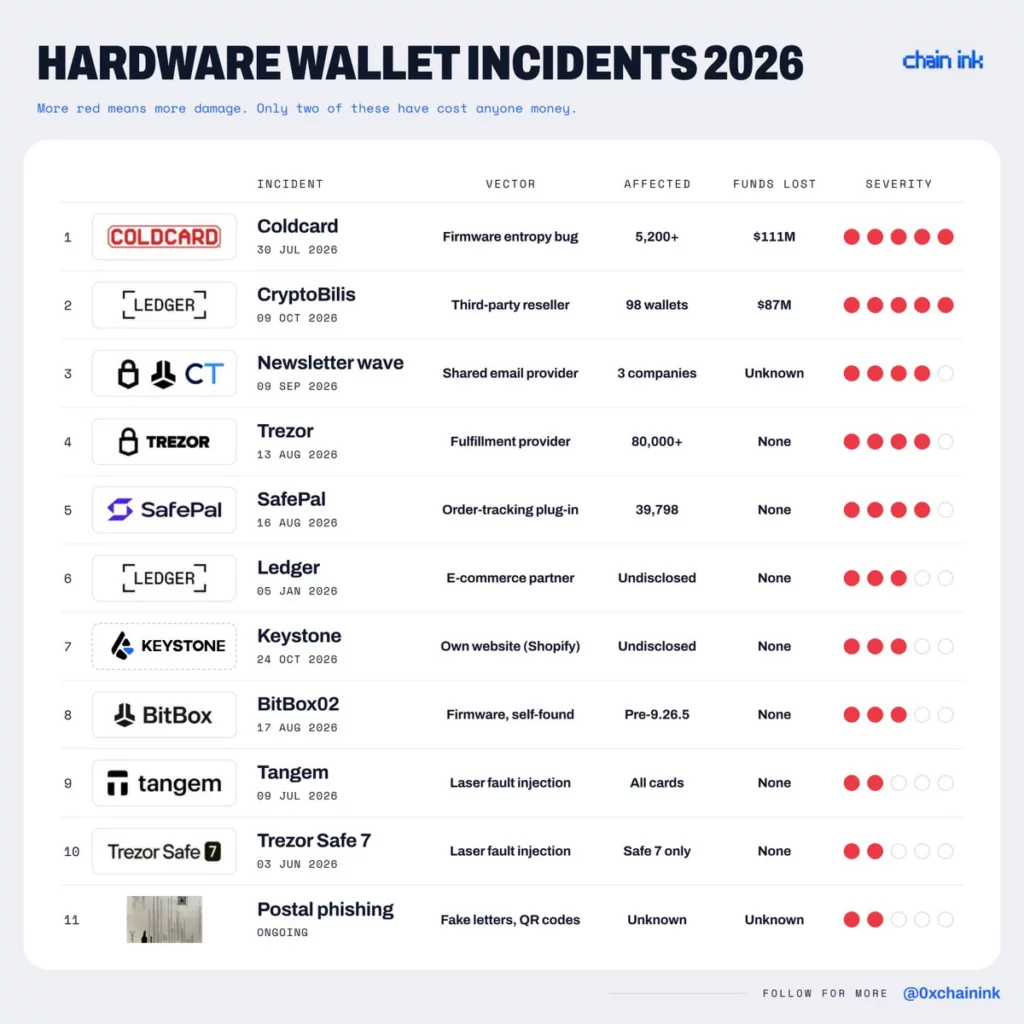
Claims that four wallet manufacturers have suffered customer data breaches this year, exposing approximately 120,000 buyers’ addresses, remain unverified against individual company disclosures.
Keystone has not published a customer count, geographic breakdown of affected orders or independent forensic findings.
Its public statement says the company is preparing a detailed incident report while contacting affected buyers through email.
